SMB1001 certification

SMB1001 certification: put the controls in place, then prove it

When a client or insurer asks how you protect their information, a list of products is not enough. We assess your gaps, implement the agreed fixes and organise the evidence for certification through CyberCert. Real Bytes holds SMB1001 Gold through CyberCert and supports businesses across Australia.

Bronze to Diamond
5 tiers
Gold, 2026 edition
27 controls
Certificate validity
12 months
Talk to an engineer 07 3114 2808
Last updated:
Official cover of SMB1001:2026, the cyber security standard for small and medium businesses
Official standard cover from Dynamic Standards International. SMB1001:2026 was released on 1 September 2025 and is updated annually.

What the certification means

SMB1001 certification: what it actually covers

DSI writes the standard

Dynamic Standards International publishes SMB1001. The current edition is SMB1001:2026, released on 1 September 2025 and updated annually to track the threat landscape. CyberCert publishes the certification requirements against it.

DSI: SMB1001:2026
Five tiers, start anywhere

SMB1001 has five levels, from Bronze to Diamond. You begin at the level that matches your context, not at Level 1. You are not required to complete all five levels, and you keep the progress of previous work when you move up.

DSI: SMB1001:2026

A matrix decides your tier

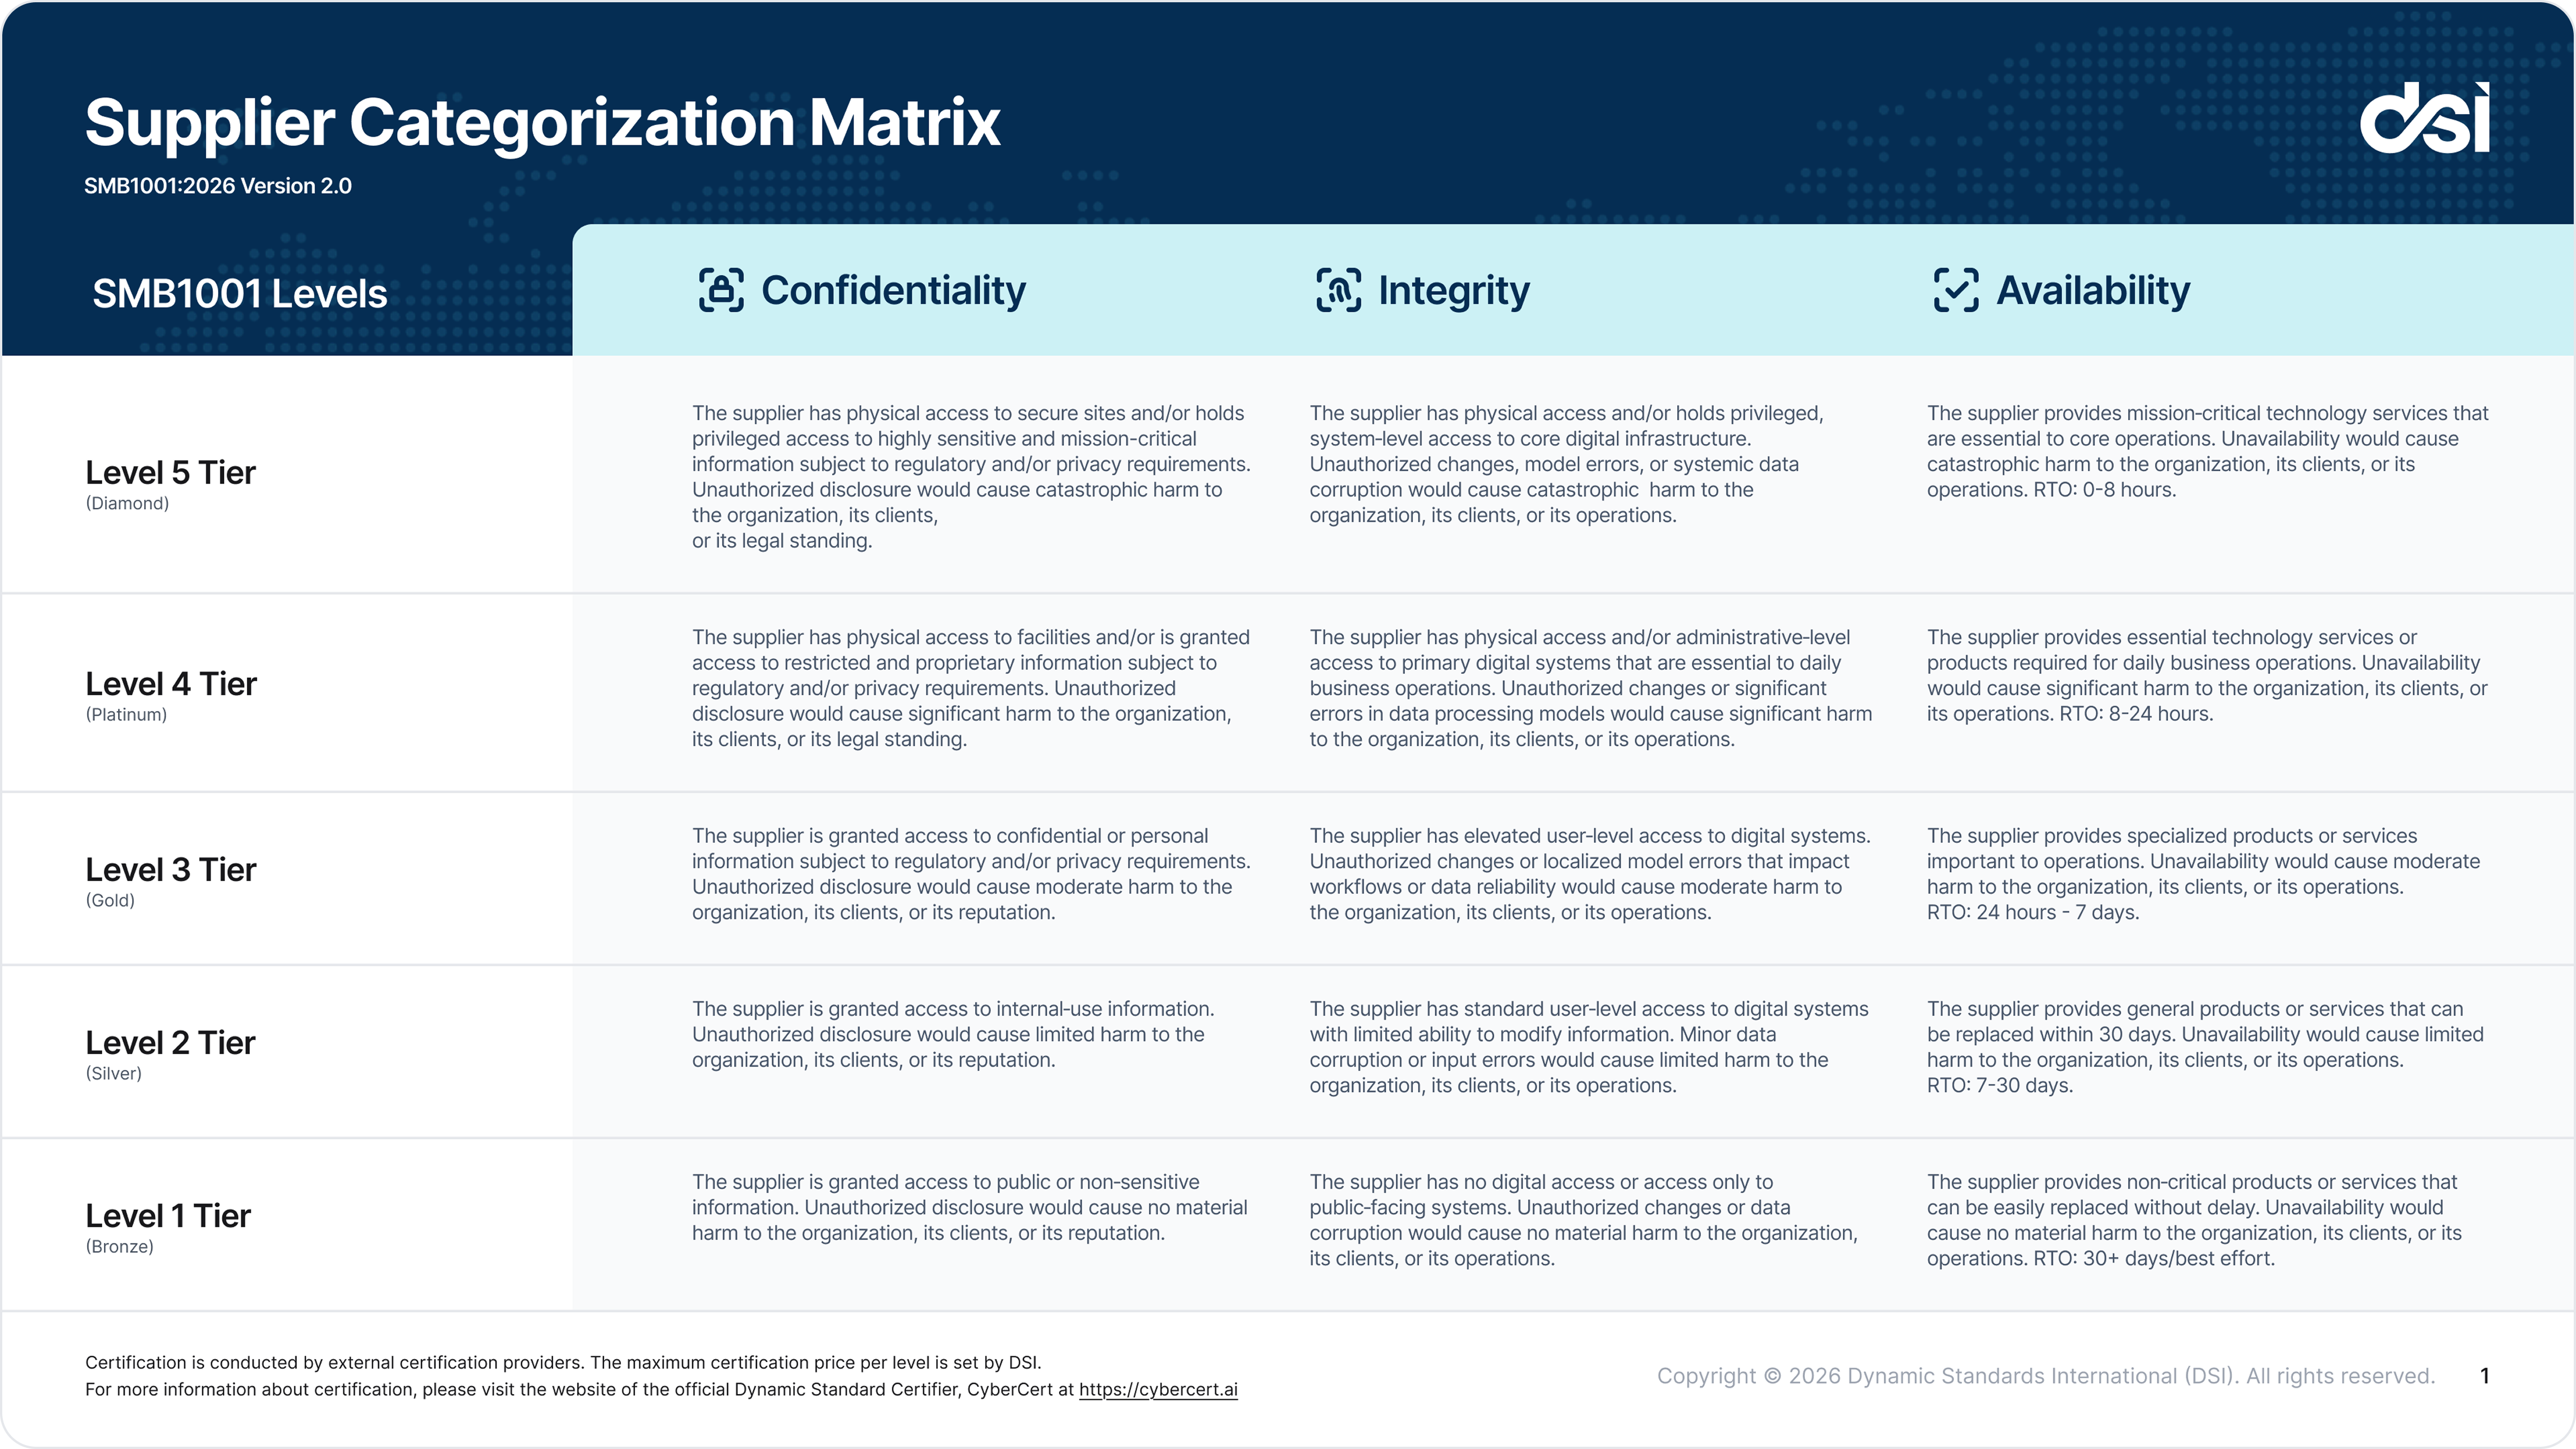
DSI's Supplier Categorization Matrix sets the right level using three factors: the information you handle, the access you hold, and how critical your service is. A customer or insurer may also specify a minimum tier in a contract or tender.

DSI: Supplier Categorization Matrix

CyberCert issues the certificate

CyberCert is the certifier. Every subscription includes a step-by-step workbook, 12 months of portal access, an attestation letter, a shareable digital certificate, a PDF certificate with a QR code, and display badges. Platinum and Diamond also require an external audit.

CyberCert: certification and pricing

It maps to other frameworks

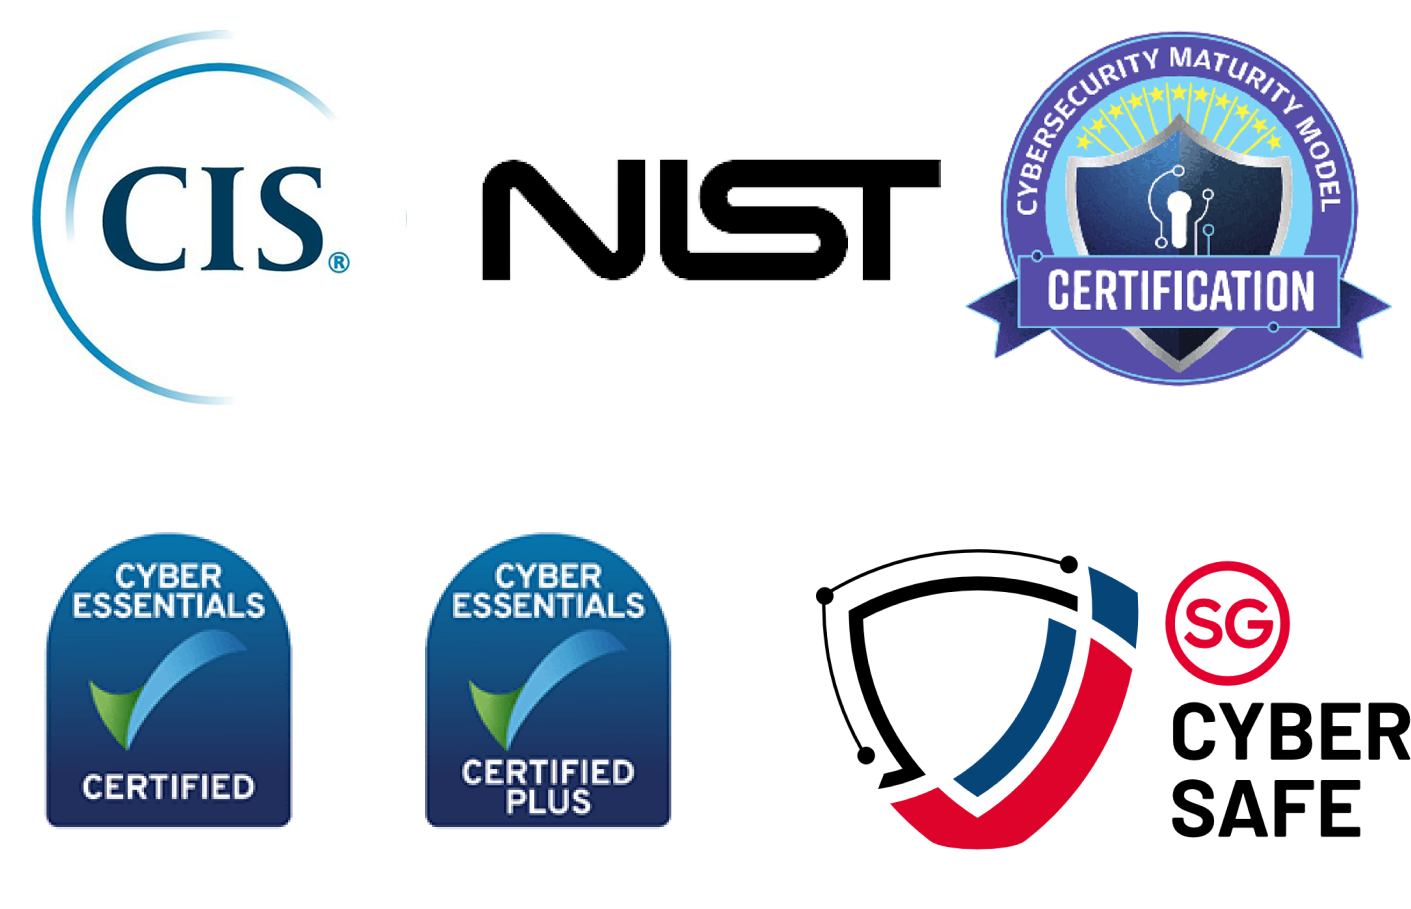
DSI has mapped SMB1001 to the United Kingdom Cyber Essentials, the United States CIS Controls and CMMC. Working towards SMB1001 also starts your alignment with those frameworks, so the effort is not wasted when a customer asks for something else.

DSI: SMB1001:2026

The five tiers

Compare the SMB1001 certification tiers

Choose the tier that matches your risk and customer requirements, not simply the highest badge. Control counts are CyberCert's cumulative SMB1001:2026 totals. The access, information and recovery time descriptions come from DSI's Supplier Categorization Matrix.

Official CyberCert Bronze tier badge

Level 1

Bronze

7 controls total

Director attested

Basic preventive controls, including firewalls and antivirus, to stop common threats before they reach your systems.

Built for a business where

Information handled
You handle public or non-sensitive information only. A leak would cause little or no material harm.
System access
You do not access client systems, or you only work on public-facing systems such as a website.
Recovery target
Your work can tolerate 30 days or more to recover, on a best-effort basis.
Official CyberCert Silver tier badge

Level 2

Silver

17 controls total

Director attested

More advanced preventive measures that add layers of protection against increasingly sophisticated threats.

Built for a business where

Information handled
You handle internal-use information. A leak would cause limited harm.
System access
You have standard user-level access to client systems, with limited ability to change information.
Recovery target
Your work should resume within 7 to 30 days of an incident.
Official CyberCert Gold tier badge

Level 3

Gold

27 controls total

Director attested

A holistic risk management approach where risks to people, processes and technology are identified, assessed and addressed in a coordinated way.

Built for a business where

Information handled
You handle confidential or personal information covered by regulatory or privacy requirements. A leak would cause moderate harm.
System access
You hold elevated user-level access to client systems.
Recovery target
Your work should resume within 24 hours to 7 days of an incident.
Read the Gold certification guide
Official CyberCert Platinum tier badge

Level 4

Platinum

32 controls total

Director attested and audited

More formal governance and risk management, with external audit requirements as well as director attestation.

Built for a business where

Information handled
You handle restricted and proprietary information. A leak would cause significant harm.
System access
You have administrator-level access to core client systems, plus physical access to their facilities.
Recovery target
Your work should resume within 8 to 24 hours of an incident.
Official CyberCert Diamond tier badge

Level 5

Diamond

39 controls total

Director attested and audited

The highest tier, with the most demanding governance, risk management and assurance requirements, and an external audit.

Built for a business where

Information handled
You handle highly sensitive, mission-critical information covered by regulatory or privacy requirements. A leak would cause severe harm.
System access
You hold privileged access to mission-critical client systems, plus physical access to secure sites.
Recovery target
Your work must resume within 8 hours of an incident.

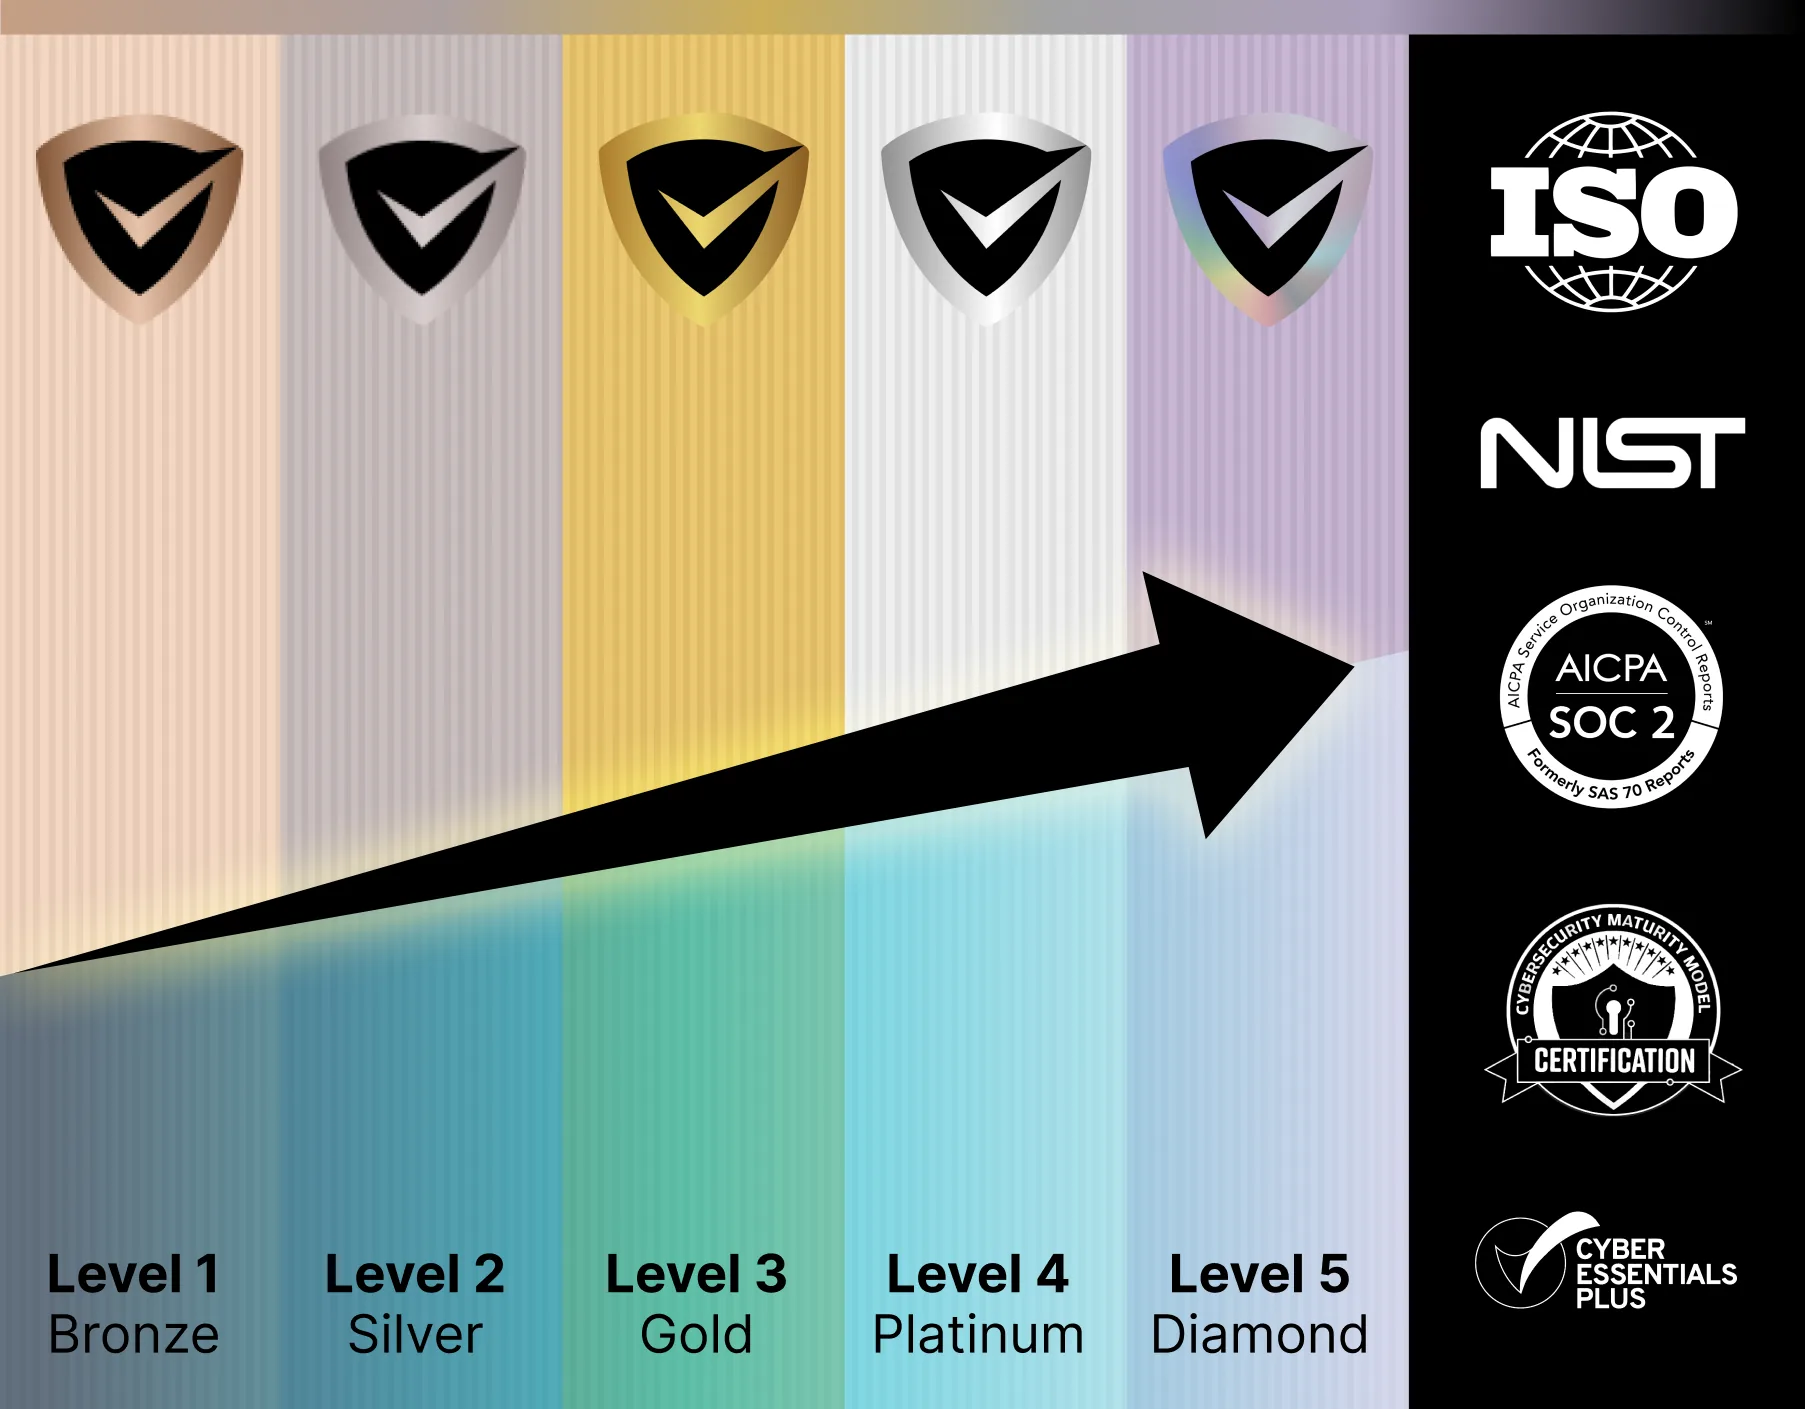
The five-tier structure behind SMB1001 certification

DSI diagram of the five SMB1001 tiers, Bronze through Diamond, showing increasing complexity and maturity
Official DSI diagram. Each level increases in complexity and maturity, but you are not required to complete all five. Sources: CyberCert 2026 counts and DSI Categorization Matrix.

How the right tier is chosen

Three factors set your SMB1001 certification tier

DSI's Supplier Categorization Matrix uses three factors to decide the right level for a supplier. A customer, insurer or tender may set a minimum on top of this, but the matrix is where the tier starts.

Confidentiality

The information you handle

From public information up to restricted and proprietary data. Suppliers handling personal or confidential information are expected to reach Gold or higher.

DSI: Supplier Categorization Matrix

Integrity

The access you hold

From no digital access through standard user access to administrator and physical access. Higher privileges call for stronger controls.

DSI: Supplier Categorization Matrix

Availability

How critical your service is

Measured by recovery time objective. A non-critical supplier may accept 30 days; an essential technology service may need to recover in under 8 hours.

DSI: Supplier Categorization Matrix
DSI Supplier Categorization Matrix mapping SMB1001 levels to confidentiality, integrity and availability factors
The full DSI Supplier Categorization Matrix, linking each tier to the information, access and service criticality a supplier handles. Read it on DSI's site.

From gap assessment to evidence

How we help you achieve SMB1001 certification

  1. 01

    Confirm the tier and the gaps

    We review the information you hold, the access you have and how critical your services are, then compare your controls with the agreed tier and edition. You get a clear gap list and the evidence each requirement needs.

  2. 02

    Agree a priced implementation plan

    You receive prioritised fixes, responsibilities and a timeline based on your actual gaps. We keep our implementation work separate from the CyberCert subscription and any external audit fees, so you can see exactly what you are approving.

  3. 03

    Put the controls in place and record evidence

    Our engineers make the agreed technical changes, help document your policies and test that protections work. We collect the configuration records, test results and supporting documents that fill out your certification workbook.

  4. 04

    Attest, certify, then maintain

    Your director or owner reviews the evidence and signs the attestation letter. For Platinum and Diamond we also prepare you for the external audit. CyberCert issues the certificate, valid for 12 months, once its requirements are met. We review changes and renewal with you so the controls do not slip between cycles.

Real Bytes implements the controls and prepares the evidence. CyberCert is the certifier. Read CyberCert's published process and inclusions.

Framework alignment

SMB1001 certification maps to the frameworks your customers ask for

DSI has mapped SMB1001 to leading international frameworks, so the work you do for one tier also starts your alignment with these. It is not a replacement for them, but it means the effort carries over.

United Kingdom

Cyber Essentials

The UK government-backed baseline for cyber hygiene. DSI maps SMB1001 to it.

United States

CIS Controls

The Center for Internet Security prioritised controls. DSI maps SMB1001 to them.

United States

CMMC

The Cybersecurity Maturity Model Certification used in US defence supply chains. DSI maps SMB1001 to it.

DSI diagram showing SMB1001 mapped to Cyber Essentials, CIS Controls and CMMC
Official DSI framework mapping. Logos are trademarks of their respective owners. Source: DSI SMB1001.

Need a separate Australian framework assessment? See our Essential Eight alignment and framework comparison guide.

Questions

SMB1001 certification questions, answered

Next step

SMB1001 certification Australia: choose the right tier, then price the work

For SMB1001 certification Australia support, talk to an engineer about your current controls and the evidence a client or insurer needs. We will confirm the target tier, applicable edition and a priced plan for closing the gaps. Not sure where you stand? Run the free SMB1001 gap assessment first. Need a separate framework assessment? See Essential Eight alignment.

Talk to an engineer 07 3114 2808

Cookie Preferences

We use cookies to improve your experience, analyse site traffic, and personalise content. By clicking "Accept All", you consent to our use of cookies. Privacy Policy

Privacy Act 1988 compliant. Your data is never sold.