
 Remote
A client or insurer wants proof we are secure
You need a certificate and evidence, not more tools. SMB1001 gives you a certificate you can show. We get you ready and handle the paperwork.
How SMB1001 certification worksFree SMB1001 gap assessmentAttackers now log in with stolen passwords, and we catch them before they reach your money. Most attacks on small businesses start with one stolen login or one fake invoice. We watch your logins, email and devices day and night, and when something happens, we own it until it is fixed. You also get the paperwork that proves it to clients and insurers.
Real Bytes is a Brisbane based managed IT and security provider, certified to SMB1001 Diamond through CyberCert. We deliver cyber security services Australia wide for businesses of 10 to 200 staff: locked-down sign-ins and email, 24/7 security monitoring with Guardz and SentinelOne, backups that survive an attack, and the evidence insurers ask for. We are based in Brisbane and work with businesses Australia-wide. In Brisbane, talk to our Brisbane cyber security team. For every layer we manage in one view, see our security tower.
Source: ASD's ACSC Annual Cyber Threat Report 2025-26. Costs are self-reported averages from ReportCyber. Read our breakdown of the report.
ASD says the easiest way into a network is with stolen usernames, passwords and sessions. Compromised accounts are now one of the most reported incident types across business, government and critical infrastructure.
AI hasn't invented new attacks. It's made the old ones faster and far more convincing, so the dodgy invoice email or the fake voice on the phone is harder to pick.
That's why every Real Bytes plan starts with the same baseline:
We flag what is out of support, plan the replacement and lock down what has to stay.
Sign-in and email logs are kept and watched, so when something happens we can see what happened.
We review the apps connected to your Microsoft 365 before they get access.
We follow ASD’s guidance and help you plan as your vendors move. ASD says to stop using traditional asymmetric cryptography by the end of 2030 or sooner.
Phishing training, identity protection and email filtering built for the convincing stuff.
The Essential Eight is now evolving into ASD Essentials. Read what changed and what it means for your business.
You need a certificate and evidence, not more tools. SMB1001 gives you a certificate you can show. We get you ready and handle the paperwork.
How SMB1001 certification worksFree SMB1001 gap assessmentStop reading and call 07 3114 2808. If you want to know what the first hour should look like before you need it, read the guide.
Read the first hour guideMost businesses do not. An engineer checks your setup against the Essential Eight (now evolving into ASD Essentials) and gives you a written list of what to fix first.
Talk to an engineerWe set it up, watch it and run it. You do not manage any of it.
We watch every staff sign-in. When one comes from an odd place or device, we block it and lock the account before anyone can read your email.
Protection on every laptop, desktop and server, watched day and night. If ransomware starts, we cut that machine off from the rest of the business.
We filter email, stop others sending mail that pretends to be you, and flag lookalike senders, so fake invoices and scam links are caught before staff see them.
We can see what leaves the business through OneDrive, SharePoint and Teams, and set sharing rules that keep work moving without leaking client files.
Short, regular training plus safe practice scam emails. Anyone who clicks gets a quick lesson, not a telling off, and you see where the weak spots are.
We check leaked password lists and your public footprint. When a staff password appears, we reset it before it is used.
Tick anything that is true. Nothing is sent anywhere, it runs in your browser.
0 of 7 gaps identified
Tick the statements that apply to your business.
Australian figures from the Australian Signals Directorate and the privacy regulator.
ASD Annual Cyber Threat Report 2025-26. OAIC Notifiable Data Breaches statistics, calendar year 2025.
Those costs are only what businesses reported losing directly. They leave out the weeks spent rebuilding and the clients who quietly do not come back.
Bigger clients, government tenders and insurers now ask for evidence. We give you something you can hand over.
Basic hygiene. The controls that stop the overwhelming majority of opportunistic attacks.
What it asks for
We hold SMB1001 Diamond ourselves through CyberCert. We prepare your evidence, fix the gaps and walk your director through sign-off.
SMB1001 certificationEight controls from the Australian Signals Directorate, scored at four maturity levels, now evolving into ASD Essentials. We check where you really sit, lift you to the level you need and carry that work forward.
Essential EightUsually SMB1001 for the certificate and the Essential Eight for the protection underneath. Our guide compares them side by side.
Compare the frameworksInsurers ask about sign-in checks, device protection, tested backups and staff training before they quote, and again when you claim. We make sure your answers are true.
Insurance readinessYour legal obligations, such as ransomware payment reporting and the Privacy Act changes, are set out on our Australian regulatory hub.
From the field

Mason Wise
MSP Practice Lead · Microsoft 365 migrations & infrastructure takeovers
On the tenant migrations, the recurring pattern was not the mailbox move itself, it was everything sitting around it. Shared mailboxes with stale delegations, Teams meetings with calendar invites pointing at the old tenant, SharePoint sites with broken external sharing links, conditional access policies that had been built up over years and nobody could explain. Each cutover was treated as a discovery exercise first, migration second. For the island NFP takeover, the network had grown organically. Mixed vendor switching, undocumented VLANs, a satellite link that was the only path off the island, and a server rack that had not had a backup tested in over a year. The risk profile was unusual because if anything went wrong, the next engineer was a boat ride away.
Tenant cutovers ran on documented runbooks with pre-stage, delta sync, and weekend cutover windows. Conditional access and identity governance were uplifted as part of the move rather than carried across as-is, so each client landed on a cleaner posture than they started with. Users opened Outlook on Monday and kept working. For the island NFP, did a full site audit in person, rebuilt the documentation from the ground up, replaced the end-of-life core switching and firewall, and put proper monitoring and remote access in place so future work does not require a site visit unless it genuinely does. The NFP now has a documented network, tested backups, and a support model that matches the realities of where they operate.
Meet the engineers behind this workWe watch your staff logins, email, laptops, servers and Microsoft 365 around the clock, and step in when something looks wrong. We also patch, check backups, review who has access, train your staff, and give you the reports that prove all of it happened.
Real Bytes managed IT with security included starts from $150 per person a month ex GST. Standalone certification work such as SMB1001 is quoted separately based on tier. See the Pricing page for detail.
SMB1001 is a certificate you can show clients, insurers and tender panels, issued through CyberCert across five tiers. The Essential Eight, now evolving into ASD Essentials, is a set of technical controls from the Australian Signals Directorate. It is not a certificate. The two overlap heavily, so most businesses do both.
It is evolving. In October 2026 ASD released the Essentials series, which launched with Enterprise IT (the evolution of the Essential Eight), Operational Technology and Cloud chapters. Both stay on cyber.gov.au while ASD works through transitional arrangements into 2027, and ASD has not published a retirement date. Keep meeting your existing obligations until regulators say otherwise. Work done against the Essential Eight is not thrown away, and we align clients to it today and carry that work into ASD Essentials.
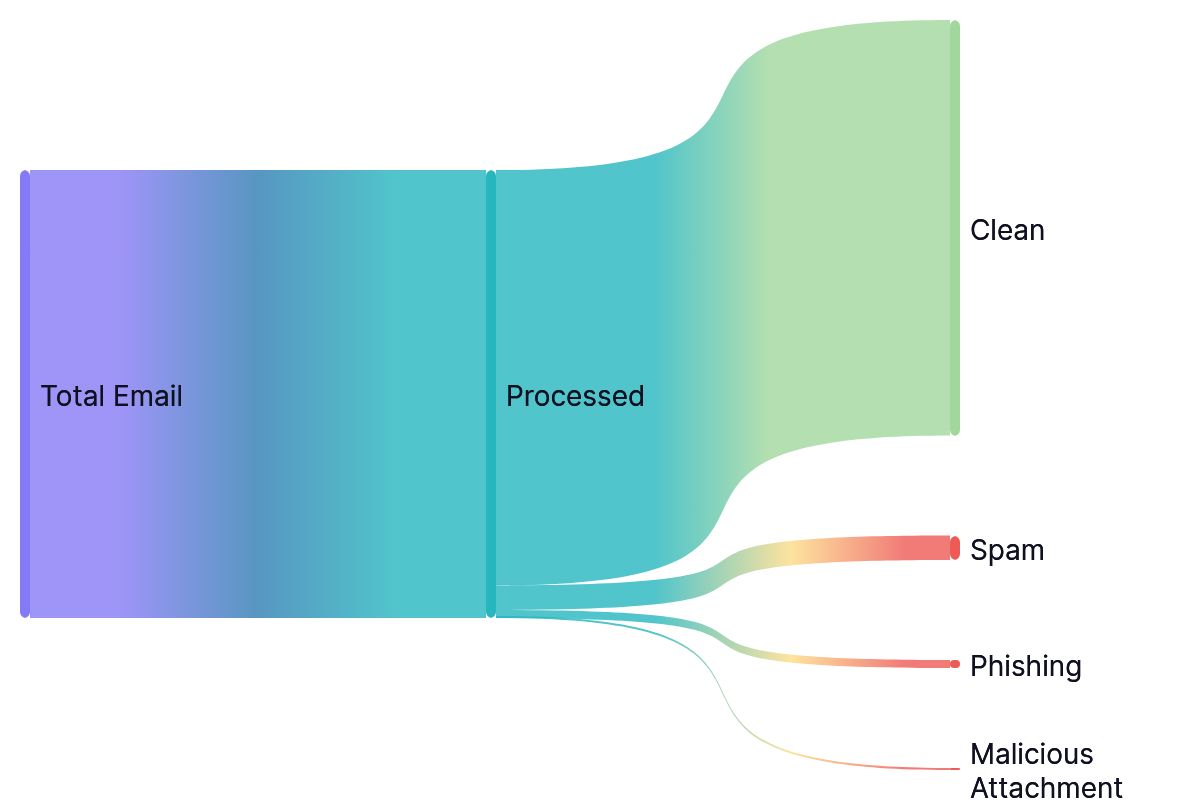
ASD received over 82,000 cybercrime reports, about one every six minutes, and small businesses reported an average cost of $55,400 per report. Compromised accounts and credentials are one of the most reported incident types, and AI is making phishing and impersonation more convincing. ASD advises small businesses to choose secure by design products, turn on automatic updates and make sure someone clearly owns security monitoring and incident response.
If your business turns over more than $3 million a year, yes. The Cyber Security Act 2024 requires you to report a ransomware or extortion payment to the Australian Signals Directorate within 72 hours. Smaller businesses have no legal duty, but reporting through ReportCyber is still worth doing.
Antivirus protects the device. Most attacks now start with someone logging in using a stolen password, and antivirus never sees that because nothing harmful runs on the laptop. You also need someone watching logins and email, which is what we do.
Yes. We deliver cyber security services Australia wide. Brisbane is home, and we work with businesses Australia-wide. A business in any Australian city gets the same engineers, the same service and the same phone number.
We cut off the affected laptop or account straight away, then call you. From there we own it until it is fixed: cleaning up, restoring what was lost, and helping with any reporting you need to do. If you are not a client and you have an incident now, call 07 3114 2808.
Done properly, staff notice an extra sign-in check on new devices and very little else. Where a control does get in the way, we explain the trade-off and let you decide.
Talk to a senior engineer. We look at what you have today, tell you plainly what an attacker would try first, and what to fix first. Same service wherever you are in Australia.