
 Remote
SMB1001 certification
Prove you are safe to work with.
Clients, insurers and tender panels now ask how you protect their information. SMB1001 gives you a straight answer: a named tier, a certificate anyone can check, and controls that actually work. We find your tier, fix the gaps, gather the evidence and get you certified through CyberCert.
Real Bytes is a Brisbane based managed IT and security provider, and we hold SMB1001 Gold through CyberCert ourselves. We help small and medium businesses get SMB1001 certified Australia wide.
 SMB1001 Gold certified ourselves
 DSI Founding Mission Supporter
 2027 Mission Supporter
- Australia wide since 2017
Trusted by
Businesses, schools and not-for-profits that already call us.


Why now
The question is coming. Have the answer ready.
82,000+
cybercrime reports made to the Australian Signals Directorate in 2025-26. About one every six minutes.
ASD$55,400
average self-reported cost of cybercrime for a small business. For a medium business it is $141,300, up 45%.
ASD1 Jan2027
the date SMB1001 becomes free for every business to read. Your clients will be reading it too.
DSI12months
how long a certificate lasts. Then you renew against the edition current at the time.
CyberCertWhat SMB1001 is
A cyber standard written for businesses your size.
Dynamic Standards International, an Australian not-for-profit and registered charity, writes SMB1001 and updates it every year. Big frameworks like ISO 27001 assume a security team and a budget to match. SMB1001 starts with the basics and adds controls in five steps, so you certify at the level your clients need and climb later without losing work you have done.
DSI does not certify anyone. CyberCert does. At Bronze, Silver and Gold a director signs an attestation that the controls are in place. Platinum and Diamond add an independent audit. Either way the result is a certificate your clients can look up online.
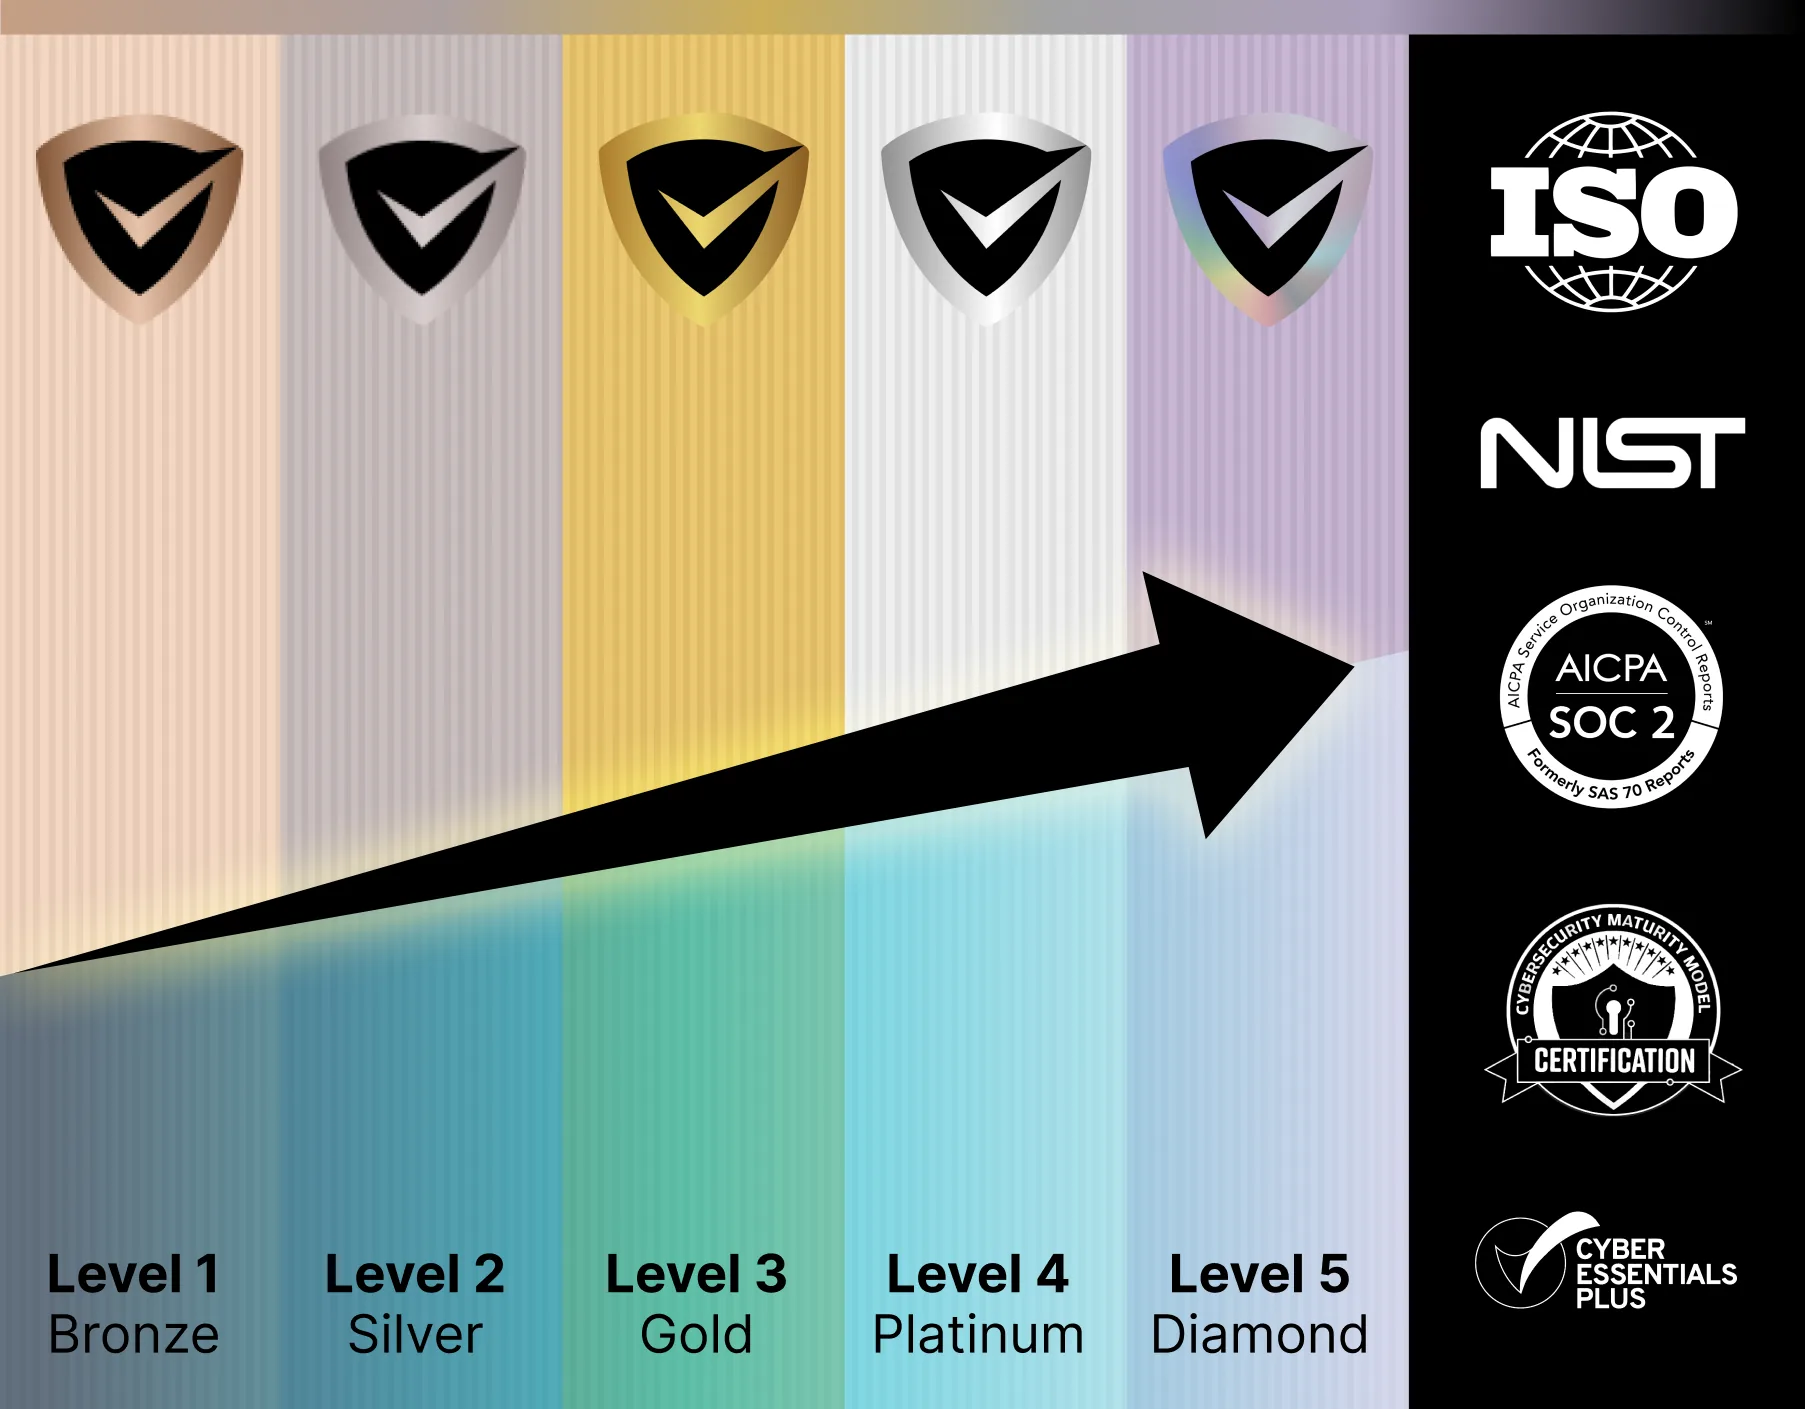
Five areas at every tier
People, process and technology. Each tier asks more of each area.
- Technology managementFirewalls, anti-malware, patching and the devices that hold your data.
- Access managementNamed accounts, multi-factor sign-in, a password manager and no everyday admin rights.
- Backup and recoveryBackups of what matters, restores that have been tested, and insurance at Gold.
- Policies, plans and proceduresInvoice fraud checks, an incident response plan, an asset register and an AI use policy.
- Education and trainingSecurity awareness for every staff member, and at higher tiers, practice runs of your response plan.
Find your tier
Three questions. One tier.
These follow DSI's Supplier Categorization Matrix, the tool large organisations use to decide what to ask of suppliers. Your highest answer sets the tier.
The five tiers
Start where you are. Climb when you need to.
Level 1
Bronze
7 controls
Director attests
You hold public information and do not touch client systems.
- A named technical support specialist
- Firewall, anti-malware and automatic patching
- Strong passwords and backups
- Security awareness training for everyone
Level 2
Silver
17 controls
Director attests
You send and receive business information and log in to client systems as a normal user.
- Multi-factor sign-in on email
- Individual accounts and no admin rights for staff
- Email anti-spoofing and an invoice fraud policy
- Server patching, a password manager and a visitor register
- Your tier
Level 3
Gold
27 controls
Director attests
You hold personal or confidential information, or elevated access. Often the tier insurers ask for.
- Endpoint detection and response
- Multi-factor sign-in on every business app and social account
- Cyber insurance, an incident response plan and an asset register
- A responsible AI use policy
Level 4
Platinum
32 controls
Director attests, plus independent audit
You are a critical supplier with admin access to core systems or access to client premises.
- Vulnerability scanning of internet facing systems
- Multi-factor sign-in on VPN, remote desktop and data stores
- Least privilege across cloud accounts
- From 2027: device management, network segmentation, application control and an AI governance framework
Level 5
Diamond
39 controls
Director attests, plus independent audit
You run mission critical services that must be back within 8 hours.
- Encryption of important data at rest
- Annual penetration and social engineering testing
- Police checks for privileged staff and a supplier trust program
- From 2027: phishing resistant sign-in for admins and control of unapproved AI tools
Totals include every lower tier. Gold means all 27 controls, not that many on top of Silver.
SMB1001:2027
What changes, and when it reaches you.
- 1 Sep 2025SMB1001:2026 releasedThe edition most current certificates are issued against.
- 1 Sep 2026SMB1001:2027 in early accessPublished to programme members ahead of general release.
- 1 Jan 2027Free to readUnder DSI's SMB1001 Unlocked, every business can download the standard at no cost.
- Your renewalYour real deadlineA current certificate runs its full 12 months. Plan for the 2027 controls before you renew.
Bronze and Silver keep the same number of controls, with clearer wording on patching, passwords and old software. The new work lands higher up.
A responsible AI use policy has been required at Gold since the 2026 edition. If you are Gold today, you should already have one.
Every 2027 change, control by control
Our evidence standard
A control counts when it covers everyone.
A screenshot of one account proves very little. We check every control against your full staff and device list. If multi-factor sign-in is on for three people and off for the rest, the control is not met, and we will not let a director sign as if it were.
The one people underestimate most is at Gold: multi-factor sign-in on every business app and every social media account, not just email. We find those accounts before an auditor or an attacker does.
How we certify you
Four stages. Clear about who does what.
Find the tier and the gaps
We doWe work out your tier from the information you hold, the access you have and how critical you are, then check every control against it. You get a gap list with the evidence each control needs.
You doTell us who your clients are and what they ask for. Forward any supplier questionnaire or tender clause.
Gather the business evidence
We doWe give you a folder structure with one subfolder per control number and a list of what goes in each.
You doAdd the business side first: policies, signed agreements, training records, the asset register and your insurance. Doing this early means our hours go on fixing, not chasing paperwork.
Fix and prove the technical controls
We doOur engineers close the gaps and capture the proof: firewall, patching, anti-malware, EDR, multi-factor sign-in, backups and email security records.
You doApprove changes that affect staff, like new sign-in prompts, and nudge anyone who lags behind.
Attest, certify, renew
We doWe walk your director through the CyberCert portal, control by control. At Platinum and Diamond we prepare you for the independent audit. Then we keep the controls running for next year.
You doYour director reviews the evidence and signs the attestation. CyberCert issues a certificate anyone can verify.
What it costs
Three costs. All quoted before you commit.
Our managed plans are built to reach a tier: Flex gets you to Bronze or Silver, Advantage to Gold, and Ultimate from Gold up to Platinum or Diamond. If you are already on one, much of the work is done.
See the plans- The certificate
CyberCert's yearly subscription: A$95 Bronze, A$195 Silver, A$395 Gold, A$595 Platinum or A$995 Diamond, plus tax if applicable. Platinum adds an A$3,000 independent audit fee and Diamond A$5,000. We pass it through at cost.
- Our certification work
A fixed fee for the gap check, evidence pack and walking your director through attestation. Quoted before you start, with no hourly charges on top.
- Closing the gaps
Depends entirely on what the gap check finds. Many controls are already in place on our managed plans, so the list is usually shorter than people expect.
We did it first
Certified ourselves before we certified anyone else.
Real Bytes holds SMB1001 Gold through CyberCert, and we are a Founding Mission Supporter of DSI's push to make the standard free. We went through the same evidence folders and the same director attestation we will walk you through.
 Philip VernerDirector
 Blake BathGeneral Manager
 Mason WiseMSP Practice Lead
 Mitchell MorganAutomation & Platform Lead
How it compares
SMB1001, Essential Eight and ISO 27001.
They overlap, but none replaces the others. Pick the one your clients ask for, then reuse the evidence.
| Question | SMB1001 | Essential Eight | ISO/IEC 27001 |
|---|---|---|---|
| What it is | A five tier standard written for small and medium businesses | ASD's eight mitigation strategies, each with maturity levels | An international standard for an information security management system |
| Certificate | Yes, issued by CyberCert and checkable online | No certificate. Assessed against the maturity model | Yes, from an accredited certification body |
| Who checks it | Director attests at Bronze to Gold. Independent audit at Platinum and Diamond | Self assessed or reviewed by an assessor | External audit, then surveillance audits |
| Updated | Every year | ASD is moving to the new Essentials series | Every few years |
| Best when | A client, insurer or tender wants proof sized to your business | A government or regulated client names it | A large client or contract names it |
DSI has also mapped SMB1001 to the UK's Cyber Essentials, CIS Controls and CMMC. For the detail, read our framework comparison guide. The Essential Eight itself is being replaced by the ASD Essentials series. Our tracker and the Essentials for enterprise IT page show which SMB1001 work carries across.
Get help your way
Six ways to reach us. Pick whichever suits you.
Helpdesk hours are Monday to Friday, 8am to 5pm AEST. On Advantage and above, emergencies get a response within 1 hour and outages within 2, with 24/7 best-effort escalation.
- Call 07 3114 2808
An engineer answers Monday to Friday, 8am to 5pm AEST. After hours, weekends and public holidays, Chip, our AI agent, answers on the same number or on 07 3180 0965, logs it and escalates urgent incidents to the on-call engineer.
Call now - Email the helpdesk
Send it to helpdesk@realbytes.com.au and a ticket is logged straight away, with a reference number you can quote.
Email us - Client portal
Log and follow your tickets, see what we are working on and who has it.
Open the portal - Remote support
When an engineer asks to see your screen, start a secure session here. You start it, so nobody sees your screen until you do.
Start a session - Chat in Microsoft Teams
Clients can message Chip, our AI assistant, in Teams to log a request without leaving their desk.
How clients reach us - Service status
Check whether Microsoft 365 or another cloud service is down before you lose an hour troubleshooting.
See live status
Questions
What people ask us.
What is SMB1001 certification?
SMB1001 is a cyber security standard for small and medium businesses, written by Dynamic Standards International, a not-for-profit. It has five tiers from Bronze to Diamond. CyberCert checks that you meet a tier and issues a certificate your clients can verify online.
Which tier do we need?
Use the three questions in the tier finder on this page. They follow DSI's Supplier Categorization Matrix: the information you hold, the access you have and how quickly clients need you back. The highest answer sets the tier. If a client, insurer or tender names a tier, that one wins.
How many controls are in each tier?
Under SMB1001:2026 the totals are 7 at Bronze, 17 at Silver, 27 at Gold, 32 at Platinum and 39 at Diamond. Under SMB1001:2027 they are 7, 17, 28, 37 and 44. The totals include every lower tier, so Gold means all 27, not 27 on top of Silver.
Is there an audit?
Bronze, Silver and Gold rest on a signed attestation from a director or owner. That is a real declaration with real weight, so the controls have to be in place. Platinum and Diamond add an independent audit, which CyberCert charges for separately.
What happens on 1 January 2027?
Two things. The standard becomes free to read under DSI's SMB1001 Unlocked, and the 2027 edition becomes generally available. A certificate you already hold runs its full 12 months. Plan for the 2027 controls before your renewal date.
If the standard is free, why pay for certification?
Free means anyone can read the requirements. Certification is still someone checking you meet them and issuing a certificate, and the real cost is putting the controls in place. We quote both before you commit.
Does SMB1001 replace the Essential Eight or ISO 27001?
No. They overlap but are not the same. In our own mapping, even Diamond covers only about half of Essential Eight Maturity Level 1, so a client that asks for the Essential Eight needs that work done as well. DSI has mapped SMB1001 to the UK's Cyber Essentials, CIS Controls and CMMC, so the effort carries across.
What do you need from us?
A director who can sign the attestation, the business evidence only you hold, such as policies, signed agreements, insurance and staff training records, and approval for changes that affect your team. We handle the technical evidence.
Next step
See how close you already are.
Run a free gap check on CyberCert's platform. Each one scores your tier and every tier below it. Then talk to an engineer about what it found.
Keep reading
- SMB1001 Gold certification The Gold controls in detail and the path to certifying.
- Every SMB1001 requirement All 39 controls for 2026 and 44 for 2027, searchable, with who does each one.
- Free SMB1001 gap check How the CyberCert gap assessments work and what the score means.
- SMB1001 for law firms Privacy Act, AML/CTF and panel evidence for legal practices.
- SMB1001 in Brisbane Local certification support from engineers you can meet.
- The ASD Essentials series What is replacing the Essential Eight and how to plan for it.
Checked 30 October 2026. Sources: DSI: SMB1001:2026, DSI: Supplier Categorization Matrix, DSI: SMB1001 Unlocked, CyberCert: certification levels, CyberCert: Real Bytes Gold certificate (verify it), ASD Annual Cyber Threat Report 2025-26. SMB1001 is a standard of Dynamic Standards International. CyberCert issues certificates. Badges belong to their owners.