
 Remote
Passwordless sign-in
Going passwordless in Microsoft 365: the right credential for each person.
Passwordless is not one product. Admins carry a FIDO2 security key, most staff use a passkey on the phone they already have, and their laptop signs them in with a face or PIN. New starters get their first passkey with a Temporary Access Pass instead of a password. Here is the plan Microsoft recommends, how we roll it out, and a builder that sizes it for your team.
Following Microsoft's phishing-resistant passwordless deployment guidance, checked 30 October 2026.
- Credential by persona
- Rollout checklist
- Recovery covered
Reviewed by Blake Bath, General Manager, on 30 October 2026.
Who gets what
Four groups, four credentials.
Every person needs a portable credential they can carry between devices, and a local one on the device they use every day.
Admins and regulated roles
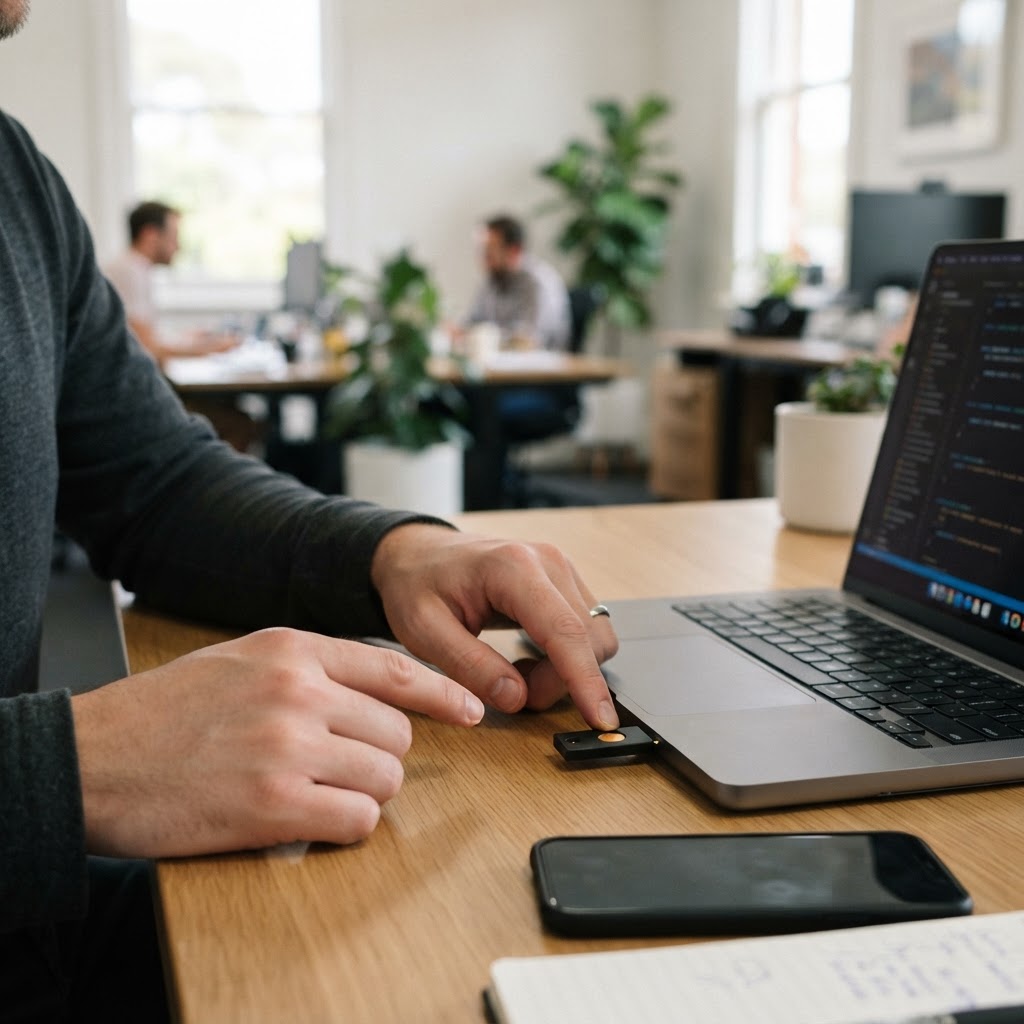
Microsoft recommends a FIDO2 security key as the portable credential, with Windows Hello for Business, Microsoft Entra passkey on Windows or a passkey in Microsoft Authenticator day to day.
- Security key to carry
- Hardware-bound, attestation possible
- Never a phone number
Staff with their own PC
A synced passkey on their phone first, then Windows Hello for Business on the PC, set up using that passkey.
- Face, fingerprint or PIN
- No password typed
- Fast once set up
Mac users
A synced passkey, then Platform Single Sign-on with the Secure Enclave key on the Mac, managed through Intune.
- Apple Passwords on macOS 13 and later
- Platform SSO through Intune
- Same passkey on their iPhone
Shared PCs and frontline staff
Microsoft Entra passkey on Windows, or a security key each. Windows Hello for Business is not for kiosks with a shared account.
- Security keys for people without a phone
- Up to 10 users per device with Hello
- No shared passwords
Passwordless plan builder
Size the rollout for your team.
Count your people by how they work. The result gives each group its credential and the number of security keys to order. Copy it as your rollout plan.
Count your people by how they work. The result gives each group its credential, following Microsoft's deployment guidance, and how many security keys to order.
Security keys to order
5for 21 people
Everyone else signs in with a passkey on a device they already have.
- Admins (2): FIDO2 security key to carry, plus Windows Hello for Business or a passkey in Microsoft Authenticator day to day.
- Staff on their own Windows PC (15): Synced passkey on their phone to start, then Windows Hello for Business on the PC.
- Staff on Macs (3): Synced passkey, then Platform SSO with the Secure Enclave key on the Mac.
- People without a suitable phone (1): A FIDO2 security key.
- Set up a Temporary Access Pass process first, for new starters and anyone who loses their only credential.
Rollout checklist
The passwordless rollout checklist.
In the order we do it. Each step follows Microsoft's deployment guidance.
- 1Find who signs in howAuthentication methods report, plus Microsoft's script for anyone still on SMS or voice.
- 2Turn on the methods in passkey profilesSecurity keys, passkeys in Authenticator and synced passkeys, scoped to the right groups.
- 3Set up Temporary Access PassFor new starters and anyone without a working method. Decide who can issue one, and how identity is checked.
- 4Admins firstSecurity keys registered and tested before anyone else moves.
- 5Portable credential for everyoneA passkey on the phone, or a key for people without one.
- 6Local credential on each deviceWindows Hello for Business on PCs, Platform SSO on Macs.
- 7Require itConditional Access authentication strengths that ask for phishing-resistant methods, starting with admins and remote access.
- 8Remove the weak methodsSMS and voice taken out of policy once people have moved.
The methods
Every passwordless method in Entra ID, compared.
| Method | Where it lives | Phishing-resistant | Best for |
|---|---|---|---|
| FIDO2 security key | A USB, NFC or Bluetooth key | Yes | Admins, shared devices, people without a phone |
| Passkey in Microsoft Authenticator | The phone, device-bound (iOS 17+, Android 14+) | Yes | Staff who want it in one app |
| Synced passkey | iCloud Keychain, Google Password Manager or another provider | Yes, no attestation | Most staff |
| Windows Hello for Business | The Windows PC | Yes | Staff on their own PC |
| Microsoft Entra passkey on Windows | A Windows device, no join needed | Yes | Shared and unmanaged PCs |
| Certificate-based authentication | Smart card or certificate | Yes | Only where required; more complex |
| Authenticator phone sign-in (push) | The phone | No | A stepping stone, not the end state |
Our view
Plan the recovery before the rollout.
The technology is the easy part now. What makes or breaks a passwordless rollout is what happens when someone loses their phone or key. If the only answer is 'call IT', the helpdesk becomes the weak point.
So we set up two things before we move anyone: a Temporary Access Pass process with a proper identity check, and a second credential for everyone who can have one. Admins get two security keys, one kept as a spare.
And we move admins first. They are the accounts attackers want most, and they are the people who will support everyone else through the change.
Mistakes we see
Five ways passwordless rollouts stall.
- Calling push approval passwordless and stoppingAuthenticator push is better than SMS but not phishing-resistant.
- No recovery planOne lost phone becomes a day of lost work.
- Windows Hello on shared accountsUse Entra passkey on Windows or keys for shared PCs.
- Leaving SMS switched on foreverAttackers pick the weakest method still allowed.
- Telling nobodyA surprise registration prompt fills the helpdesk.
How we roll it out
Passwordless in five stages.
- Step 1Assess
Methods in use, devices, shared PCs and who has admin rights.
- Step 2Prepare
Passkey profiles, Temporary Access Pass and recovery process.
- Step 3Admins
Security keys issued, registered and required.
- Step 4Everyone else
Registration campaign, help on hand, Windows Hello and Mac sign-in.
- Step 5Enforce
Phishing-resistant authentication strengths required; weak methods removed.
Related guides
Passwordless is the destination. These get you there.
The SMS retirement is pushing every Microsoft 365 tenant this way anyway.
- SMS MFA retirementThe February 2027 deadline.
- Passkeys explainedFor staff, in plain English.
- Authenticator on a new phoneWhat moves and what does not.
- Conditional Access libraryRequiring phishing-resistant MFA.
- Intune guideWindows Hello for Business and Mac sign-in.
- Identity and accessPasswordless rolled out for you.
Get help your way
Six ways to reach us. Pick whichever suits you.
Helpdesk hours are Monday to Friday, 8am to 5pm AEST. On Advantage and above, emergencies get a response within 1 hour and outages within 2, with 24/7 best-effort escalation.
- Call 07 3114 2808
An engineer answers Monday to Friday, 8am to 5pm AEST. After hours, weekends and public holidays, Chip, our AI agent, answers on the same number or on 07 3180 0965, logs it and escalates urgent incidents to the on-call engineer.
Call now - Email the helpdesk
Send it to helpdesk@realbytes.com.au and a ticket is logged straight away, with a reference number you can quote.
Email us - Client portal
Log and follow your tickets, see what we are working on and who has it.
Open the portal - Remote support
When an engineer asks to see your screen, start a secure session here. You start it, so nobody sees your screen until you do.
Start a session - Chat in Microsoft Teams
Clients can message Chip, our AI assistant, in Teams to log a request without leaving their desk.
How clients reach us - Service status
Check whether Microsoft 365 or another cloud service is down before you lose an hour troubleshooting.
See live status
Questions
What people ask about passwordless and FIDO2.
What is the difference between a synced and a device-bound passkey?
A device-bound passkey stays on one device, like a security key or a passkey in Microsoft Authenticator. A synced passkey is stored in a passkey provider such as iCloud Keychain or Google Password Manager and is available on the user's other devices. Microsoft says to treat synced passkeys as phishing-resistant, but they do not support attestation.
Which passwordless method should admins use?
Microsoft's deployment guidance recommends FIDO2 security keys as the portable credential for admins and highly regulated users, with Windows Hello for Business, a passkey in Microsoft Authenticator or certificate-based authentication as the everyday local credential.
Is Microsoft Authenticator phone sign-in phishing-resistant?
No. Microsoft says push-based phone sign-in with number matching is convenient but not phishing-resistant. A passkey stored in Microsoft Authenticator (iOS 17 and later, Android 14 and later) is.
How do new staff get their first passkey without a password?
With a Temporary Access Pass. Microsoft recommends issuing one so a new user can register their first phishing-resistant credential, ideally a portable one like a passkey on their phone, and then set up Windows Hello on their PC.
Can shared PCs go passwordless?
Yes, but not with Windows Hello for Business on a shared account. Microsoft recommends Microsoft Entra passkey on Windows or portable credentials such as security keys for shared devices. Windows Hello for Business supports up to 10 users per device.
Is passwordless really faster?
Microsoft's analysis of its consumer accounts found a password sign-in can take up to 24 seconds on average, a passkey around 8 seconds, and a synced passkey around 3 seconds.
Next step
Ready to stop typing passwords?
Tell us how many people, devices and admins you have. An engineer will lay out the plan, the keys to order and the order to do it in.

Keep reading
- SMS MFA retirement Dates and options.
- Passkeys explained For staff.
- Identity and access Our identity service.
- Microsoft 365 licensing Which plans include Conditional Access.
Reviewed by Blake Bath, General Manager, on 30 October 2026. Methods, personas, requirements and the sign-in time figures (from Microsoft consumer account data) from Microsoft Learn, checked 30 October 2026. Two keys per admin is our advice, not a Microsoft requirement. Microsoft Learn, Plan a phishing-resistant passwordless deployment; Microsoft Learn, Get started with phishing-resistant passwordless; Microsoft Learn, Enable passkeys (FIDO2) in Microsoft Entra ID; Microsoft Learn, Passwordless authentication with Intune; Microsoft Learn, Passkeys by default and SMS and voice retirement